Iran's TAG-182 group intensifies cyber surveillance efforts, leveraging MarkiRAT malware to exploit dissidents and foreign adversaries.
Increased Cyber Activity from TAG-182
Insikt Group has surfaced alarming insights regarding the TAG-182 threat cluster, revealing its ramped-up activity. This group is leveraging MarkiRAT malware, which has been instrumental in assisting the Iranian government with its extensive surveillance operations. The targeted campaigns primarily focus on Iranian citizens, both within the country's borders and abroad. Unsurprisingly, tactics employed by TAG-182 include deploying fake VPN applications and misleading offers for downloads, all designed to ensnare unsuspecting victims. Notably, social media platforms—Instagram, in particular—appear to be focal points for these malicious endeavors.
As global tensions surrounding Iran's relations with countries like the United States and Israel have lessened since April 2026, one might expect a corresponding decrease in internal surveillance efforts. However, this isn't the case. Instead, Iran's security apparatus has redirected its focus toward bolstering cyber capabilities, especially aimed at monitoring dissidents and potential foreign informants. Following a partial restoration of internet services in Iran on May 26, 2026, TAG-182's surveillance operations seem poised to intensify as it increases its efforts to track and identify dissenters. For readers interested in understanding specific indicators of compromise, a detailed analysis can be found in Appendix A. Critical defensive measures are elaborated in Appendices C and D.
Key Findings
- TAG-182 is embedded in Iran’s extensive surveillance framework, distributing MarkiRAT via deceptive Android applications that masquerade as legitimate VPNs and media services aimed at gathering intelligence.
- The latest analysis of MarkiRAT reveals striking methodological similarities to previous variants associated with the group Ferocious Kitten. This includes the use of Background Intelligent Transfer Service (BITS) techniques. However, while there are hints of operational ties between TAG-182 and Ferocious Kitten, confirming a definitive link requires further scrutiny.
- As internet access in Iran has been partially restored, a surge in surveillance operations is expected. This is particularly significant given the rising concerns about internal dissent and potential uprisings. Iranian intelligence agencies seem to be prioritizing digital surveillance as a means to enhance their security operations.
Malware Analysis and Operational Tactics
The emergence of malware samples associated with MarkiRAT in early 2026 highlights the ongoing challenges facing Iranian activists and human rights advocates. Historically, MarkiRAT has been linked to surveillance strategies targeting those who oppose the government. Among the key indicators of compromise (IoCs) tied to this campaign, TAG-182 appears to have established a custom website for an application called “YESHICA,” as evidenced in Table 1. These lures are troubling, particularly since the application “Pis2ray VPN” shows no legitimate presence on major app platforms like Google Play or the Apple App Store. This emphasizes the need for increased vigilance amongst users in the region—many may inadvertently download what they believe to be trustworthy software, only to end up compromising their digital security.
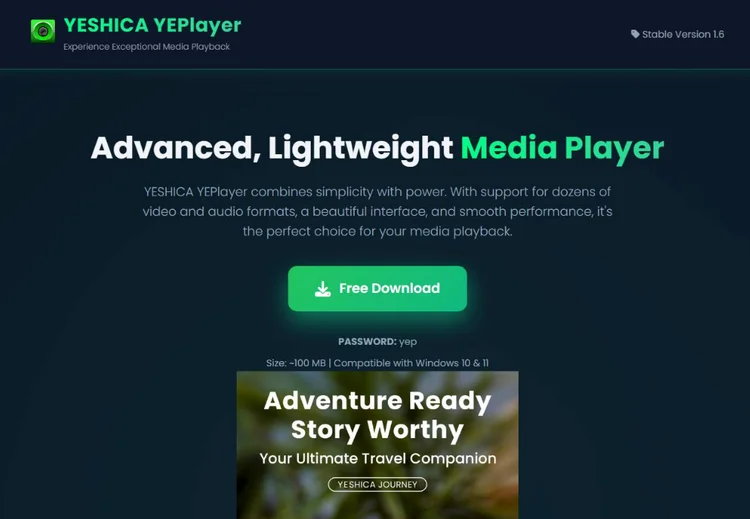
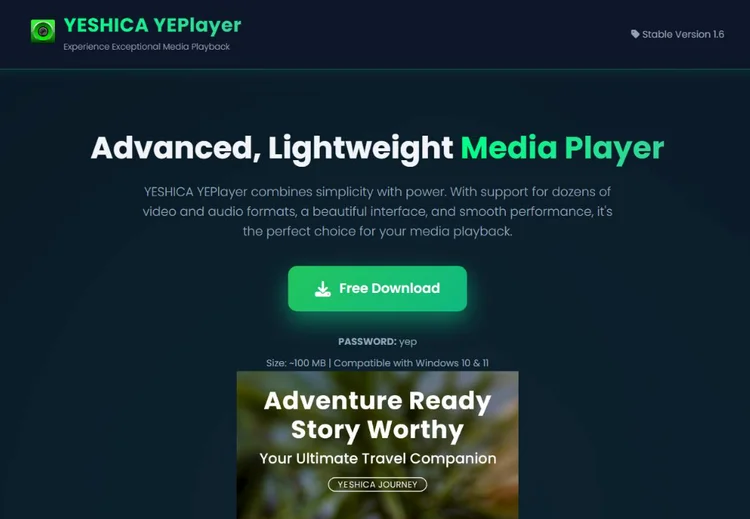
In a further twist, a novel sample linked to TAG-182's operations was unveiled in March 2026. It featured a media player branded almost identically to “YESHICA,” now labeled “YESHICA YEPlayer,” as depicted in Figure 1. This branding tactic isn't just clever; it’s indicative of the group's adaptability in circumventing detection as it continues targeting users. It reflects a deep understanding of consumer behavior and trends, leveraging the popularity of media applications to ensure a higher download rate.
The Broader Implications
The surge in surveillance activities by TAG-182 raises critical concerns about freedom and safety within Iran. The close ties between malware, social media manipulation, and the state's objectives cannot be overlooked. As the Iranian government refines its cyber capabilities, ensuring citizen privacy will become increasingly elusive, especially for those expressing dissent or activism—two activities that could easily label them as threats in the eyes of the regime.
What this means for you, particularly if you're engaged in digital rights, cybersecurity, or related fields, is the urgency to prepare for heightened digital threats in areas where government oversight is traditionally lax. This isn't merely a regional issue; the methods employed by TAG-182 could serve as a blueprint for similar operations elsewhere. We've seen it before: regimes learning from one another’s tactics, evolving at an alarming pace.
And yet, it's essential to remain a step ahead. The situation calls for not just technological responses, but also robust conversations on digital rights on a global scale. (And this is the part most people overlook) The advancements in digital surveillance technologies should not be allowed to outpace the discourse on personal freedoms and individual rights.



Discussion
Sign in to join the discussion.